Use arrow keys to navigate through slides. Press Space or Enter to pause autoplay.
Powerful VPS Servers
Full control, flexible configuration, and high-performance environment for your projects
VPS plans
Lag-free Minecraft Hosting
Play with friends on your own server - high stability, complete freedom of settings.
Minecraft plans
Dedicated Servers
Rent a full-fledged server - maximum resources, no compromises or limitations.
Dedicated plans
Reliable Web Hosting
Launch your website in minutes - fast, stable, with 24/7 support
Web Hosting plans
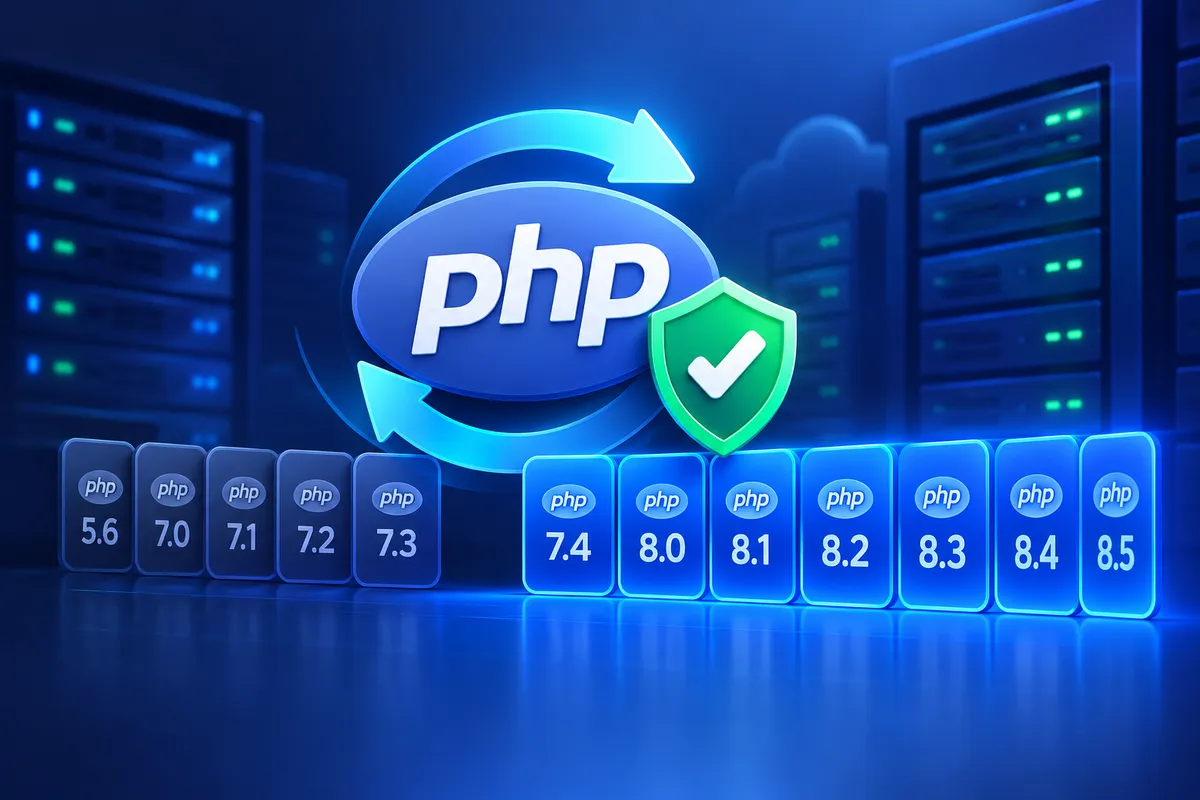
Legacy PHP versions restored
28
Related news
Following the critical PHP vulnerabilities disclosed on 21 October (CVE-2026-109618 and CVE-2026-109619), we temporarily withdrew the PHP versions for which no security fix was available.
Our platform vendor has now backported those fixes to PHP 5.6 through 7.3, in addition to the patched builds for 7.4 through 8.5 released last week. We have deployed these across our web hosting infrastructure, and all PHP versions from 5.6 to 8.5 are available again, each running a build patched against both vulnerabilities.
The same update also addresses CVE-2026-111497 in the Brotli extension, which has been updated to Brotli 1.2.1 for PHP 7.0 and later.
What this means for you
If your website was moved to a newer PHP version during last week's emergency response, it can be switched back. Contact our support team and we'll do it for you.
If your site has been running normally, no action is required.
A note on legacy versions
PHP 8.1 and older no longer receive general security support from the PHP project. The builds we run are patched against these specific vulnerabilities, but the next flaw in an unsupported branch may not get the same treatment – backports like this one are not guaranteed.
We will keep these versions available for applications that need them. We also strongly recommend moving to PHP 8.2 or later when you can, and we're happy to help you plan and test the upgrade.


